Intent-Based Networking Comes to the American Campus: When Policy, Not the CLI, Runs the Building
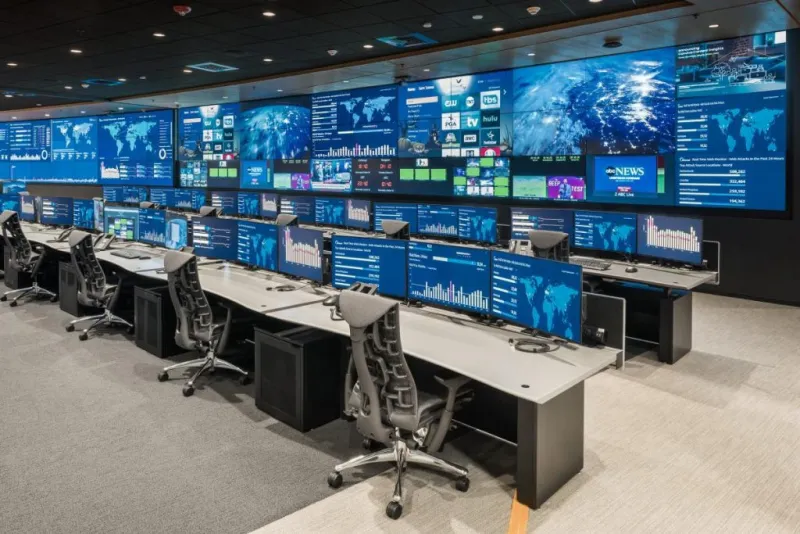
Photo: modern enterprise network operations center with servers and monitors, via constanttech.com
Walk into the headquarters of a mid-sized insurer in Columbus, Ohio, and the network operations center looks much like it did fifteen years ago: racks of switches, a wall of monitors, and an engineer with a terminal window open, typing the same VLAN commands she has typed a thousand times. But somewhere between that terminal and the access layer, something fundamental has changed. The configuration she writes is no longer the final word — it's a suggestion, handed off to a controller that decides, in real time, how every packet should flow.
This is intent-based networking (IBN), and after a decade of vendor promises, it has finally become practical for American enterprise campuses. The question is no longer whether declarative policy can replace manual configuration. It's whether network teams are ready for what that replacement means — including the uncomfortable scenario of a controller failure.
From Commands to Outcomes
Traditional network management is imperative. You tell each device exactly what to do, device by device, interface by interface. A campus with 400 switches means 400 opportunities for a typo, a skipped step, or a config drift that nobody notices until something breaks.
Intent-based networking flips the model. Instead of specifying how, the engineer declares what: which users can reach which resources, what security posture each device class must have, what segmentations must exist. The controller — Cisco's DNA Center and Catalyst Center, Juniper's Mist, Aruba Central, and HPE and Cisco rivals in this space — translates that declaration into device-level configuration, verifies that the network actually matches the stated intent, and continuously reconciles the two.
The shift is comparable to what happened in software development when infrastructure-as-code displaced hand-provisioned servers. Nobody manually racks a VM anymore; nobody should manually configure 400 access ports, either.
A Practical Walkthrough: Quarantining IoT
Consider a requirement that lands on nearly every US enterprise network team this year: IoT devices must be isolated from the corporate network. Badge readers, HVAC sensors, smart displays, the vending machine in the break room — none of them should be able to touch a file server or an employee laptop.
In the imperative world, this means creating new VLANs, configuring DHCP scopes, defining ACLs or firewall rules, updating trunk ports, and repeating the process across every access switch — then hoping nobody plugs a new sensor into an unconfigured port.
With an intent-based controller, the workflow looks different:
- Define the policy abstractly. In the controller, create a group — call it "IoT" — and a rule: IoT devices may reach the internet and nothing else. No corporate subnets, no peer-to-peer between IoT devices.
- Classify devices. The controller profiles endpoints automatically using MAC OUI matching, DHCP fingerprinting, and deep packet inspection. A printer identifies itself; the controller assigns it to the IoT group without a ticket being filed.
- Push and verify. The controller generates the segmentation — often using Scalable Group Tags (SGTs) or VXLAN-based microsegmentation — and deploys it across the fabric. Critically, it then verifies the intent, continuously checking that traffic flows match policy and flagging any deviation.
- Report in business terms. When the CISO asks whether IoT devices are isolated, the answer comes from the controller's compliance dashboard, not from a week of manual audit work.
The same pattern extends to guest access, PCI-scoped segments for retail locations, and HIPAA-driven isolation in healthcare campuses. The policy is written once; the controller enforces it everywhere, on every switch, forever.
The Question Nobody Wants to Ask: What Happens When the Controller Dies?
Here is where the editorial enthusiasm needs a caveat. In a controller-based campus, the brain sits outside the forwarding path — but the brain is still where policy lives, where changes are made, and where visibility is concentrated.
The good news: most modern controller architectures are designed with this failure in mind. Data plane traffic continues forwarding even if the controller is unreachable, because the switches hold their downloaded configurations and, in fabrics like SD-Access, continue enforcing SGT policies locally. A controller outage typically means no new changes and reduced visibility — not a dark building.
The less-good news: degraded modes are where dormant problems surface. Consider the realistic failure modes:
- Onboarding stops. New devices, new employees, new sensors cannot be classified or authenticated if classification depends on a controller that isn't answering. In a hospital, that's a problem.
- Changes go dark. An engineer who needs an emergency ACL change may find the only path is SSH-ing into individual switches — exactly the manual work the platform was purchased to eliminate, now performed under pressure by people who haven't done it in years.
- Reconciliation surprises. When the controller returns, it may discover that manual changes were made during the outage and silently overwrite them — or, worse, that its view of the network no longer matches reality.
Mature deployments mitigate this with controller redundancy across data centers, documented break-glass procedures, and — crucially — engineers who still know how the underlying devices work. A campus that has forgotten imperative networking entirely has traded one dependency for another.
The Bottom Line for Campus Teams
Intent-based networking is not vaporware anymore, and for US enterprises juggling hybrid work, exploding IoT counts, and audit-driven segmentation requirements, the operational math favors it. Declaring policy once and letting a controller enforce it across 40 buildings beats touching every switch by hand.
But the controller is a tool for leverage, not a substitute for understanding. The teams getting the most from IBN treat it as an automation layer atop deep networking knowledge — not a replacement for it. The building may run on intent, but the intent still has to come from someone who knows what the network is actually doing.